 Getly
AI Tools & Scripts
Agentic Code Security Audit - Source-to-Sink Data Flow Analyzer
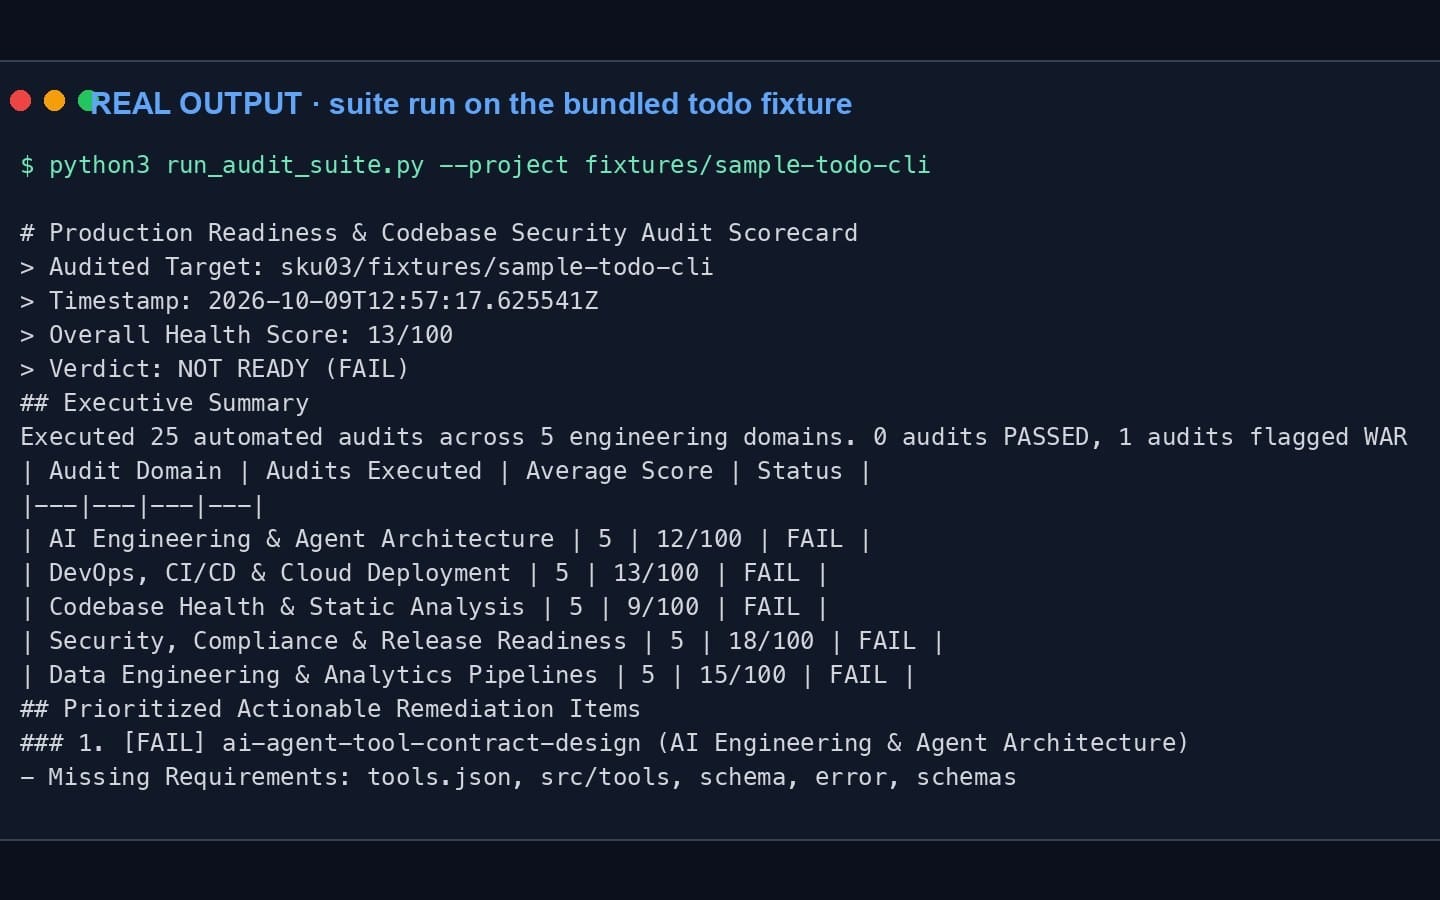
Source-to-sink data-flow analysis for AI agent and LLM codebases. Tracks untrusted input from source to dangerous sink, plus OWASP Top 10 and LLM01-LLM10 checks with scored file:line findings. Includes runnable audit CLIs.
What you get: 1 file · 32.34 KB · ZIP
See purchase optionsProduct description
Agentic Code Security Audit is a production-ready security audit skill plus two runnable Python tools your AI agent uses to find real vulnerabilities in LLM and agent codebases.
WHAT YOU GET
- SKILL.md: a seven-phase audit methodology covering OWASP Top 10 (injection, auth, XSS, SSRF, insecure design, crypto, logging, deserialization), the OWASP LLM01-LLM10 agentic risks (prompt injection, sensitive info disclosure, tool hijacking, excessive agency), privilege escalation, supply chain, severity scoring, finding templates and SOC 2 evidence tables.
- agentic_audit_tool.py: a static scanner that walks any repo and flags injection, auth bypass, hardcoded secrets, secrets in logs, unbounded loops and prompt-injection sinks across 7 languages, printing file:line findings with severity, CWE reference and remediation.
- taint_tool.py: a source-to-sink data-flow analyzer. It tracks untrusted input (request args, env, user input, file/DB reads) as it flows through variables and function calls until it reaches a dangerous sink (os.system, eval, exec, SQL, shell=True, pickle, file write), and reports the full variable chain. This catches real injection and RCE paths a regex scan misses.
WHY IT MATTERS
AI agents that call tools, run code or chain LLM output are a new attack surface. This skill gives your agent a repeatable, evidence-backed way to audit that surface, with findings you can drop straight into a security review or SOC 2 report.
HOW TO USE
Give the skill to a coding agent (Claude Code, Cursor, or any agent that reads SKILL.md), point it at a repo, and it runs the audit. Or run the tools directly from the CLI. Works offline, no API keys, no external calls.
What you get
1 file · 32.34 KB
- agentic-code-security-audit.zipZIP · 32.34 KB
AI Tools & Scripts
Agentic Code Security Audit - Source-to-Sink Data Flow Analyzer
Source-to-sink data-flow analysis for AI agent and LLM codebases. Tracks untrusted input from source to dangerous sink, plus OWASP Top 10 and LLM01-LLM10 checks with scored file:line findings. Includes runnable audit CLIs.
Free demo, no purchase needed
Included in Getly ProGet Pro
Tags
Frequently asked questions
Do I get access instantly?
Yes. This is a digital product - you can download it right after checkout, straight from your library.
Can I use it for commercial projects?
Personal use only. Use it for yourself - not in work you sell or hand to a client - and do not resell or redistribute the file.
What's your refund policy?
You can request a refund within 30 days. If something isn't right, request it from your order and the Getly team reviews it.
What file formats and sizes will I get?
You'll download 1 file - ZIP - 32.34 KB in total.
Do I get free updates?
Yes - when the seller ships a new version, you can re-download the latest files from your library at no extra cost. Check the changelog for recent updates.
Price
$2.00